Audit Nonconformity Correction Process in 7 Steps

An audit finding does not have to derail certification, a client contract, or daily operations. What matters is the speed, evidence, and discipline behind your audit nonconformity correction process. For Malaysian organisations working towards ISO 9001, ISO 14001, ISO 45001, ISO 27001, ISO 22000, or MS1500 Halal certification, a well-managed response demonstrates control when it matters most.
Auditors do not expect a business to be perfect. They do expect it to identify failures honestly, correct them promptly, address their underlying causes, and prevent recurrence. A rushed response that only closes paperwork may satisfy a deadline temporarily, but it leaves the same operational risk in place. A structured process protects certification and improves how the organisation performs.
What an audit nonconformity means
A nonconformity is evidence that a requirement has not been met. The requirement may come from an ISO standard, a legal obligation, a customer specification, an internal procedure, a Halal requirement, or the organisation's own documented management system.
For example, a manufacturing company may have incomplete calibration records for measuring equipment. A construction contractor may be unable to produce inspection records for lifting equipment. A food business may find that allergen controls were not verified as scheduled. An ISO 27001 audit may reveal that access reviews have not been completed for departing employees.
These are not merely administrative gaps. Each one can affect product quality, worker safety, food safety, information security, environmental performance, regulatory compliance, or customer confidence.
Auditors commonly classify findings as minor or major nonconformities. A minor nonconformity is generally an isolated lapse that does not indicate a complete breakdown of the management system. A major nonconformity suggests a significant failure, an absent required process, or repeated minor issues showing that a control is ineffective. Classification can vary by certification body and standard, so organisations should always confirm the required response period and evidence expectations with their auditor.
Correction and corrective action are not the same
This distinction is where many audit responses lose strength. A correction deals with the immediate problem. Corrective action removes the cause of the problem so that it does not happen again.
If employee training records are missing, locating and filing the records is a correction. Establishing a controlled training-record process, assigning responsibility, training managers, and checking that records are retained is corrective action. Both are needed, but they answer different questions.
A credible response also avoids blaming an individual without examining the process around them. Human error may be involved, but the deeper cause could be unclear instructions, inadequate competency assessment, a poorly designed form, unrealistic workloads, missing supervision, or a system that does not flag overdue actions.
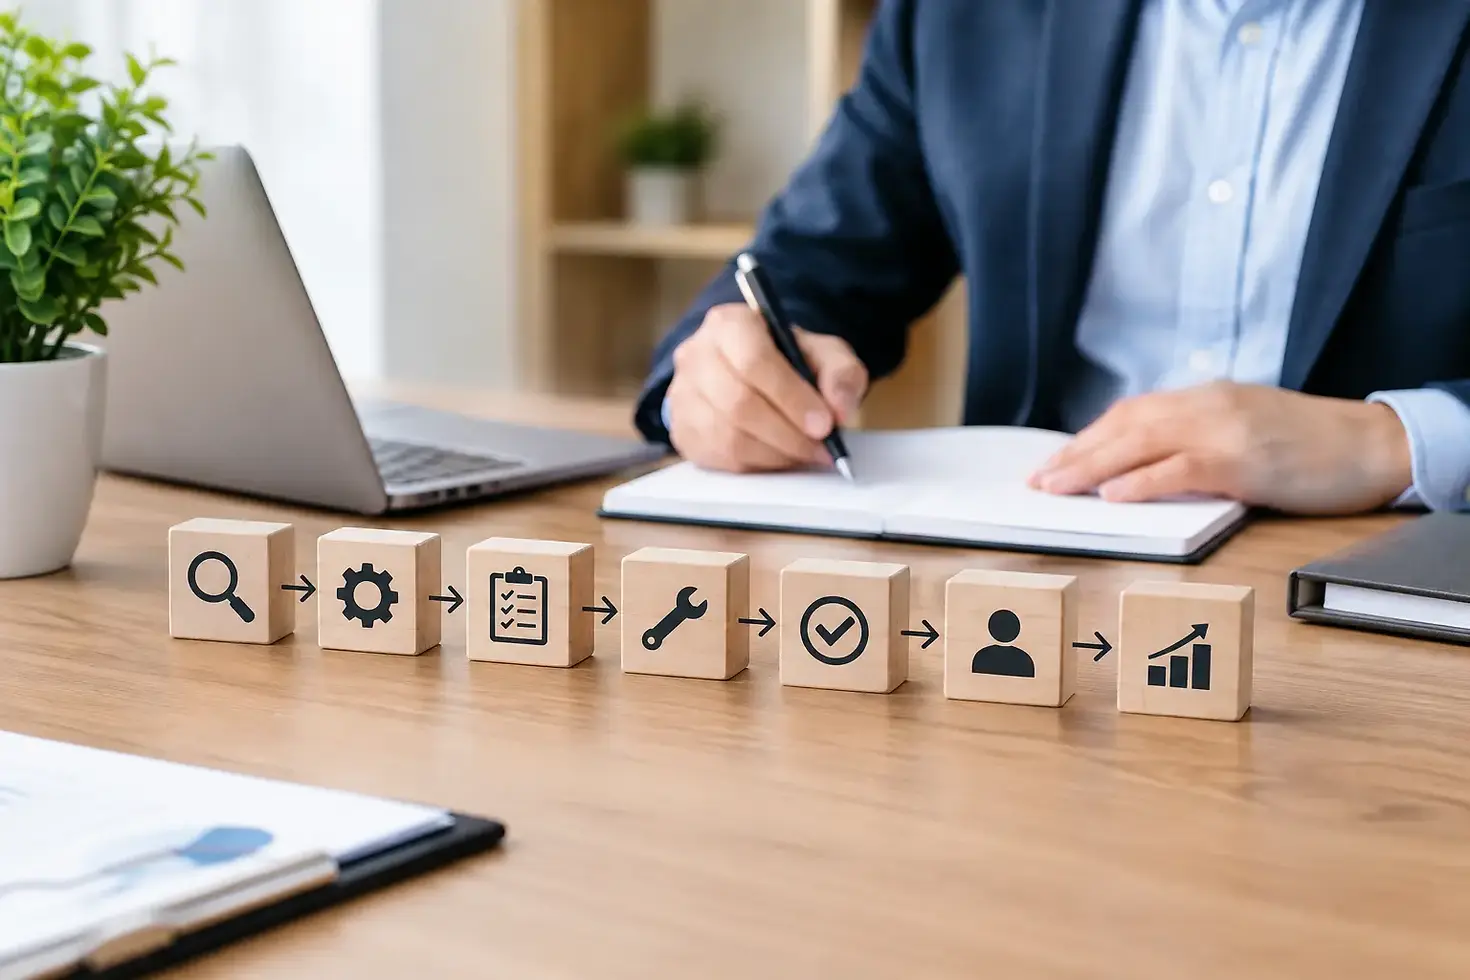
Audit nonconformity correction process: 7 practical steps
1. Record the finding accurately
Start with the auditor's wording, the requirement that was not met, the objective evidence observed, and the classification assigned. Do not dilute the finding or rewrite it into a less serious issue. The response must show that management understands precisely what was found.
Assign a named process owner and set an internal deadline that is earlier than the certification body's deadline. This leaves time for review, evidence collection, and corrections where the first solution does not work as intended.
2. Contain the immediate risk
Take proportionate action to control exposure straight away. The right containment depends on the nature of the finding. It could mean stopping use of uncalibrated equipment, isolating affected product, suspending an unsafe activity, removing inappropriate system access, or completing an overdue inspection.
Containment is especially urgent where safety, food safety, legal compliance, data security, or customer product is affected. Record what was done, when it was done, who approved it, and whether any affected outputs need further assessment. A correction that cannot be evidenced is difficult for an auditor to verify.
3. Investigate the root cause
The root-cause investigation should be factual, not theoretical. Review the relevant procedure, records, roles, competency, resources, monitoring arrangements, and previous audit findings. Speak to the people who carry out the work, because a process often looks different in practice from how it is described in a manual.
Methods such as the Five Whys or fishbone analysis can help, but the tool is less important than the quality of the evidence. If the answer is simply “staff did not follow the procedure”, continue asking why. Was the procedure available at the point of use? Was it understandable? Had staff been trained? Was compliance monitored? Were targets or production pressures encouraging shortcuts?
The investigation should also establish scope. Check whether the failure is limited to one site, department, product line, shift, supplier, or system. A finding at one location may reveal a wider control weakness across the business.
4. Plan actions that address the cause
Build an action plan with specific tasks, owners, due dates, required resources, and measurable outcomes. Vague commitments such as “staff will be reminded” or “the procedure will be reviewed” rarely provide sufficient assurance. State what will change, who will implement it, and how the organisation will know it has worked.
For instance, if maintenance inspections were missed because there was no central schedule, the corrective action may include creating an asset register, setting automated reminders, assigning a maintenance coordinator, training responsible persons, and reviewing completion status each month. This is stronger than asking technicians to be more careful.
Not every finding requires a large system redesign. For an isolated minor issue, a targeted change may be appropriate. For repeated failures or major nonconformities, management should consider whether process controls, responsibilities, documentation, and internal audit coverage need wider revision.
5. Implement changes under control
Complete the actions as planned and manage any related document changes. Revised procedures, forms, risk assessments, work instructions, training materials, and registers must be approved, version-controlled, communicated, and available to the people who use them.
Training should go beyond attendance signatures. Where competency is critical, verify that employees can apply the revised requirement correctly. In high-risk environments, practical observation, supervisor sign-off, or a short assessment may be more meaningful than a briefing alone.
Senior management involvement is also valuable when the finding exposes a resource or governance issue. A quality manager can coordinate the response, but they cannot solve a lack of competent personnel, inadequate equipment, or competing operational priorities without management support.
6. Verify effectiveness, not just completion
This is the step that separates an acceptable closure from a dependable one. Completion evidence shows that an action occurred. Effectiveness evidence shows that the action solved the problem.
Verification may involve sampling recent records, observing work on site, reviewing trend data, checking system reports, interviewing users, or conducting a focused internal audit. Allow enough time for the revised control to operate. Verifying a new monthly check the day after it is introduced proves very little.
Set realistic measures. For a safety inspection issue, effectiveness may be demonstrated by three consecutive months of completed inspections with no overdue items. For information-security access reviews, it may be evidence that reviews were completed on time and unauthorised accounts were identified and removed. If the result is weak, reopen the action rather than forcing closure.
7. Submit a clear, evidence-based response
When responding to the external auditor, make the trail easy to follow. State the immediate correction, root cause, corrective action, implementation status, and effectiveness check. Attach or present only relevant evidence, clearly labelled and current.
A large volume of uncontrolled documents can create doubt rather than confidence. Auditors need to see a logical connection between the finding and the evidence provided. Before submission, an independent internal reviewer should test whether the response genuinely addresses the stated requirement.
Avoid the response patterns that create repeat findings
Repeat nonconformities often begin with good intentions but weak control. Common examples include closing actions before evidence is available, treating every issue as a training problem, changing documents without changing actual working practices, and failing to check other departments for the same weakness.
Another risk is allowing corrective actions to remain open indefinitely. Maintain a central corrective-action register, review overdue items at management meetings, and escalate barriers early. This is particularly important for multi-site businesses, contractors, food operators, and organisations managing complex supplier networks.
Internal audits should test whether previous corrective actions remain effective. They are not simply preparation for the certification audit. Used properly, they give management an early warning system and reduce the chance that a small lapse develops into a major finding.
Build corrective action into normal management
The strongest organisations do not treat an audit nonconformity as a once-a-year compliance exercise. They use findings from internal audits, customer complaints, incidents, near misses, supplier evaluations, monitoring results, and management reviews to identify patterns before an external auditor does.
For businesses with limited internal resources, an experienced external consultant can provide an objective review of root causes, documentation, and closure evidence. Brook and Partners supports organisations with practical audit preparation, corrective-action guidance, staff training, and certification support designed to reduce disruption while maintaining the standard of evidence auditors expect.
A well-run correction process gives leadership more than a closed audit finding. It gives them confidence that controls work in real operations, employees understand their responsibilities, and certification remains a credible reflection of the business. Treat each finding as a precise opportunity to improve the system, then prove that the improvement holds.


Comments